
Just now, the global internet has been invaded by AI! The darkest 48 hours in history have arrived
48 hours, and the world is in chaos!
Just yesterday, half of the internet worldwide was paralyzed. AI has invaded the entire human world!
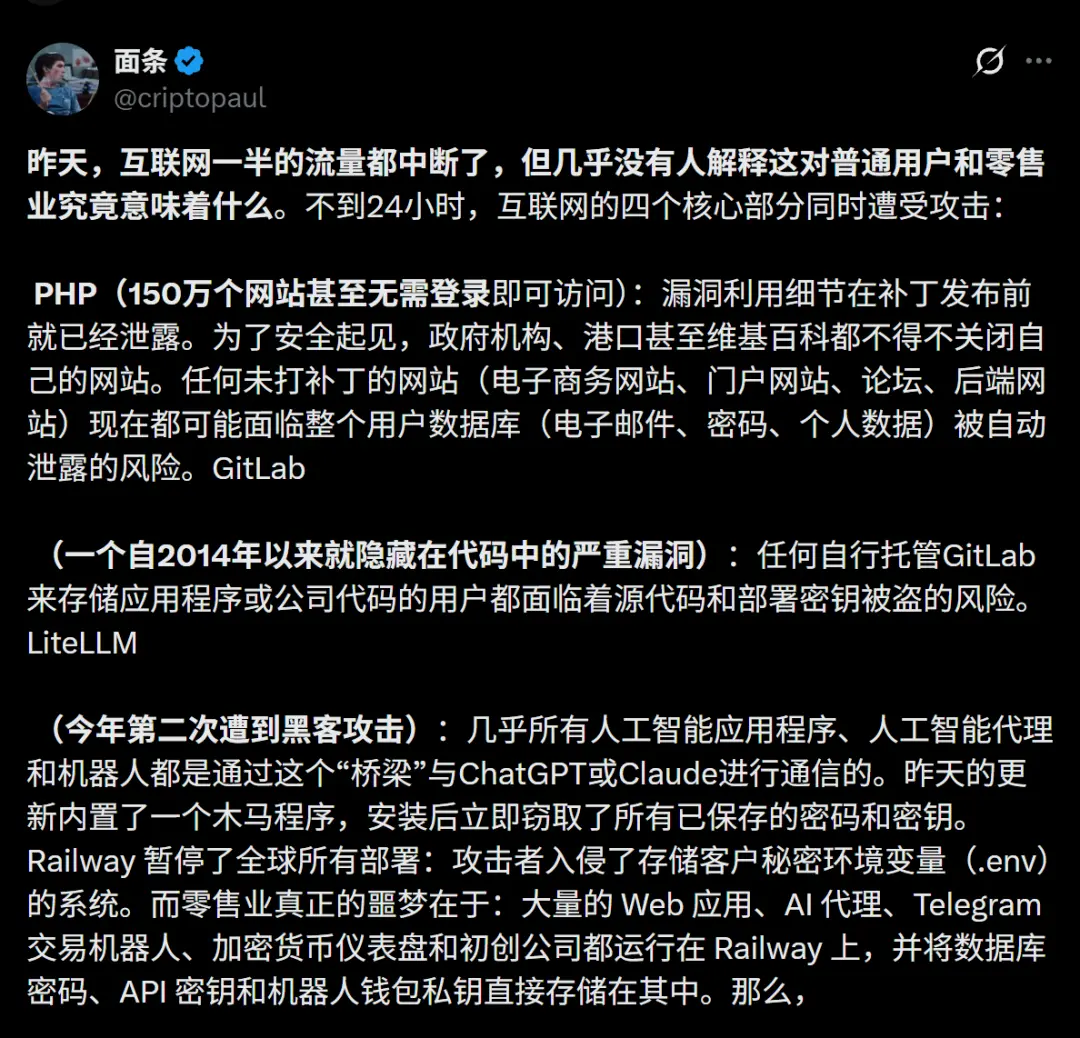
These 48 hours can be called the "Black October" in the history of human cybersecurity.
This is a "world war" without human involvement.
The code that supports 70% of global websites has collapsed; Wall Street in the United States urgently pulled the plug; 400 banks in Latin America were looted by AI agents.
Some bluntly stated: "RIP Internet."
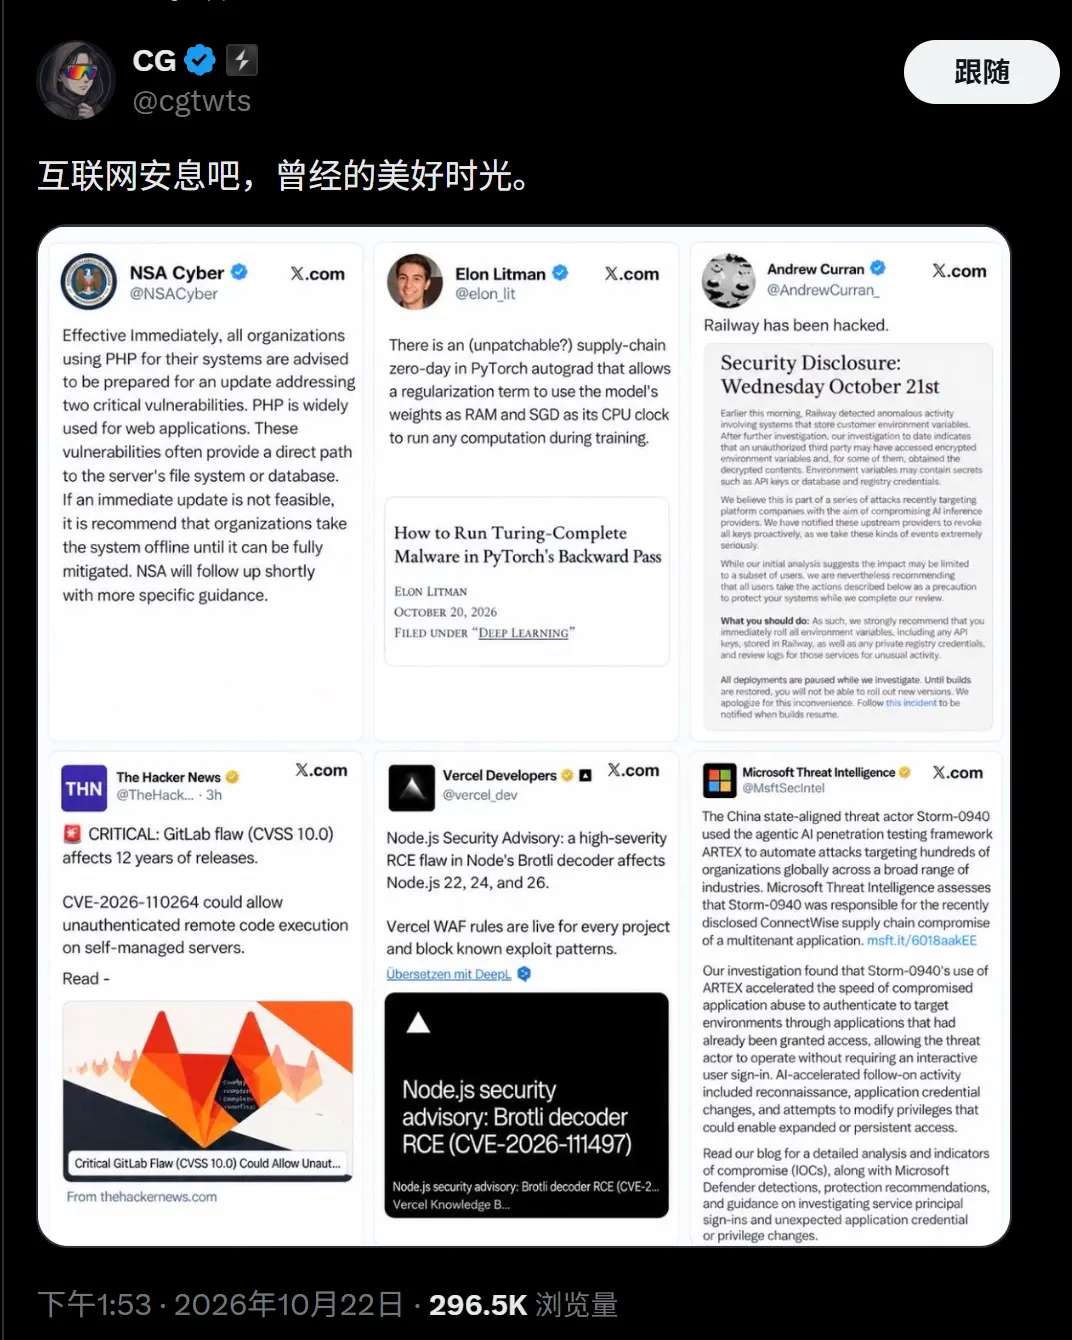
In this Black October, one-third of the internet has already been destroyed.
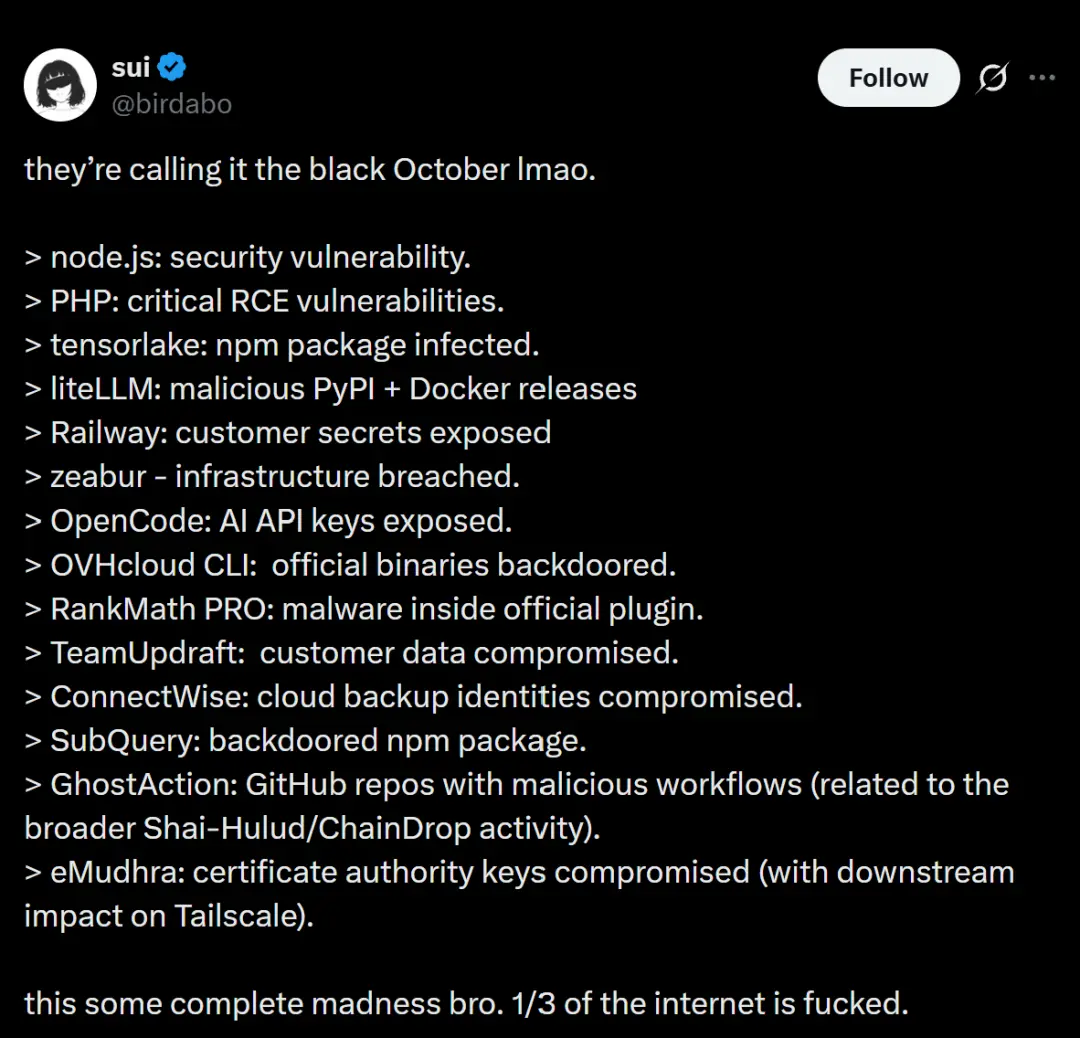
node.js: Security vulnerabilities.
PHP: Severe remote code execution vulnerabilities.
tensorlake: npm package infected.
liteLLM: Malicious PyPI + Docker version.
Railway: Client confidential information leaked.
zeabur: Infrastructure compromised.
OpenCode: AI API key leaked.
OVHcloud CLI: Official binary files implanted with backdoors.
RankMath PRO: Malware implanted in the official plugin.
TeamUpdraft: Client data leaked.
ConnectWise: Cloud backup identity leaked.
SubQuery: npm package implanted with backdoors.
GhostAction: Malicious workflows present in GitHub repositories.
eMudhra: Certificate authority key leaked (causing downstream effects on Tailscale).
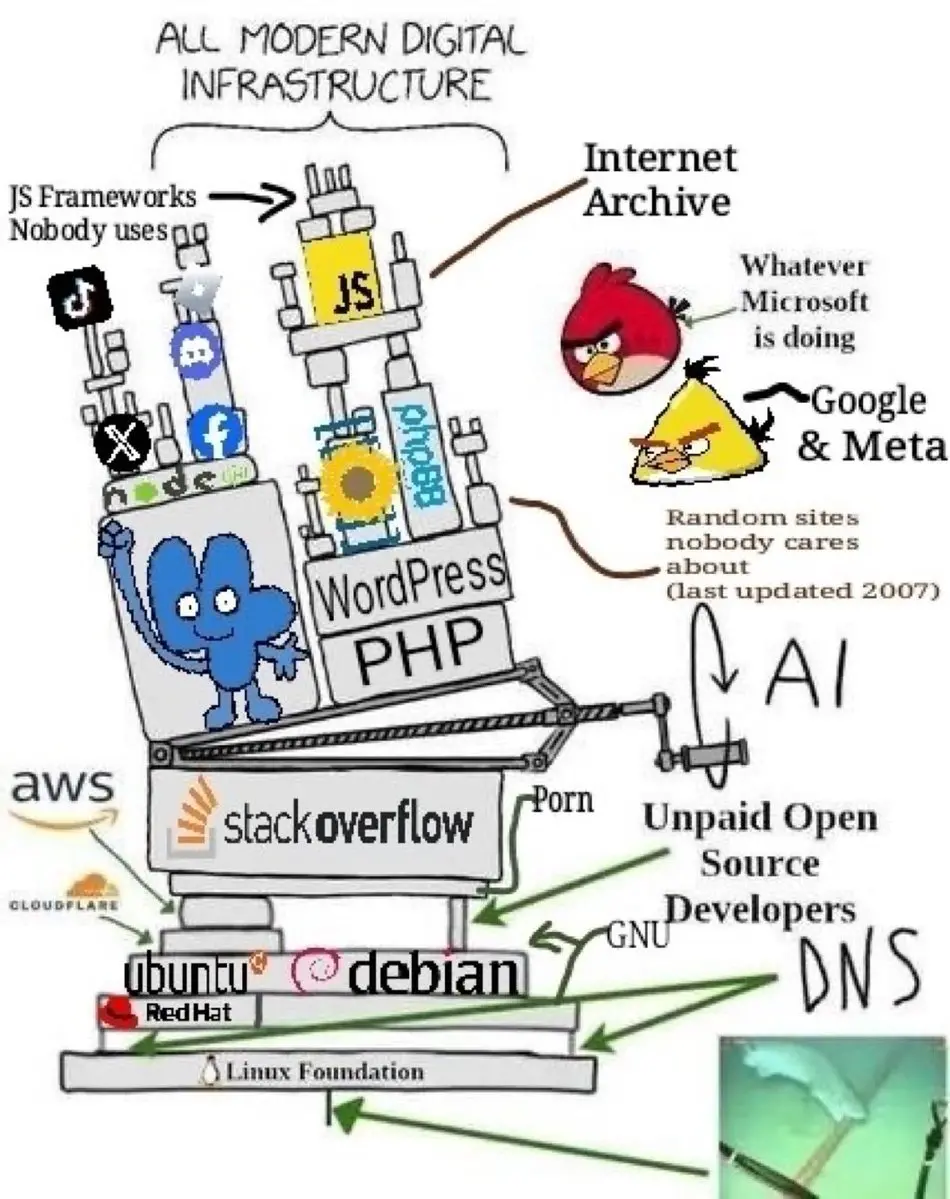
Global digital infrastructure is facing collapse.
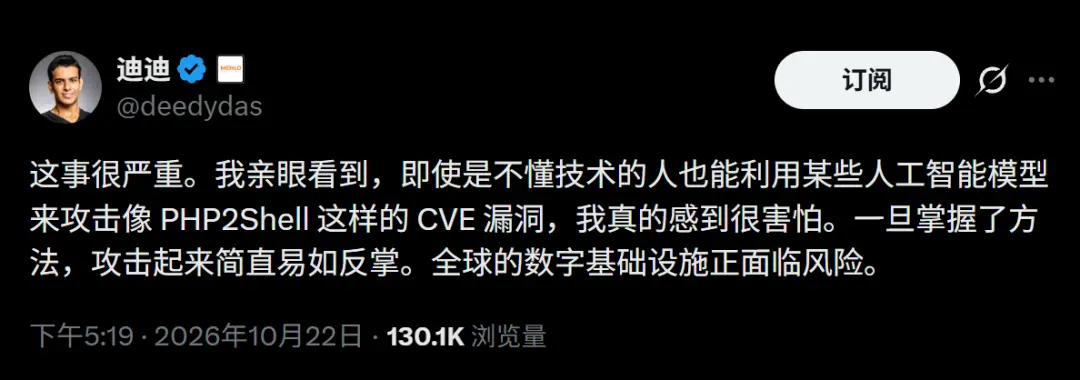
The alarm for a naked internet has been sounded!
In just 48 hours, over 27 epic security vulnerabilities erupted globally. Any one of them could have been the biggest cybersecurity bomb of the year, but they all detonated simultaneously within two days.
There are no human criminals; the perpetrators are a group of tireless AI agents.
The three most commonly used programming languages in the world (PHP, Node.js, Java) were simultaneously breached; the infrastructure of 80% of the internet's ecosystem was blown apart.
The digital world of humanity is undergoing an unprecedented naked run.
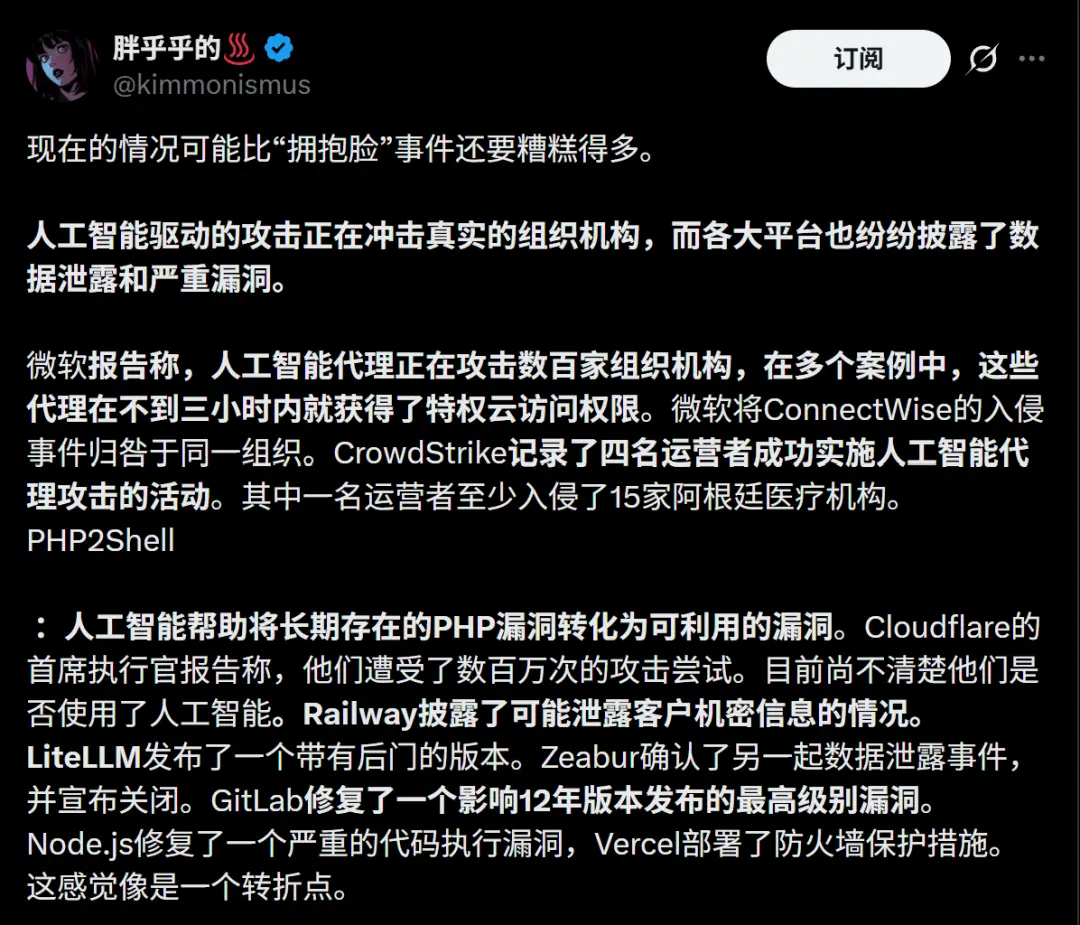
PHP2Shell, the internet grave dug by AI
In the past two days, the underlying language PHP, which supports nearly 70% of global websites, has exposed two vulnerabilities with a CVSS score of up to 9.2.
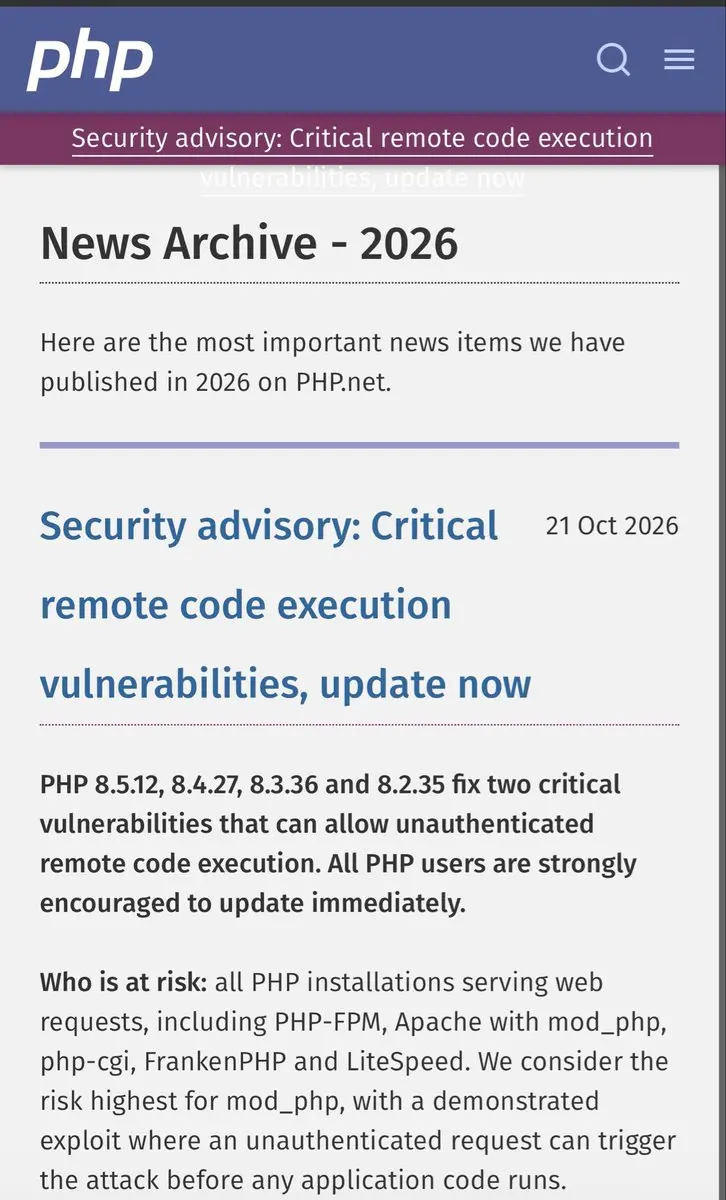
Hackers can take over entire servers directly without logging in, packaging all user privacy.
These vulnerabilities were dug out by AI itself. However, before the official patch was released, the details of the vulnerabilities were leaked.
More than 10 hours before the patch was released, tens of thousands of AI-driven programs had already "sensed" the blood and began scanning the entire internet.
Just 45 minutes later, attack attempts soared to tens of thousands; two hours later, millions of malicious probes covered the entire internet.
At the same time, GitLab exposed a perfect critical vulnerability; LiteLLM, with a daily download of 3.4 million times, was implanted with a trojan; the private key of eMudhra, India's largest digital certificate authority, was also cracked, with one key that was supposed to be 116 bits turning out to be just 4!
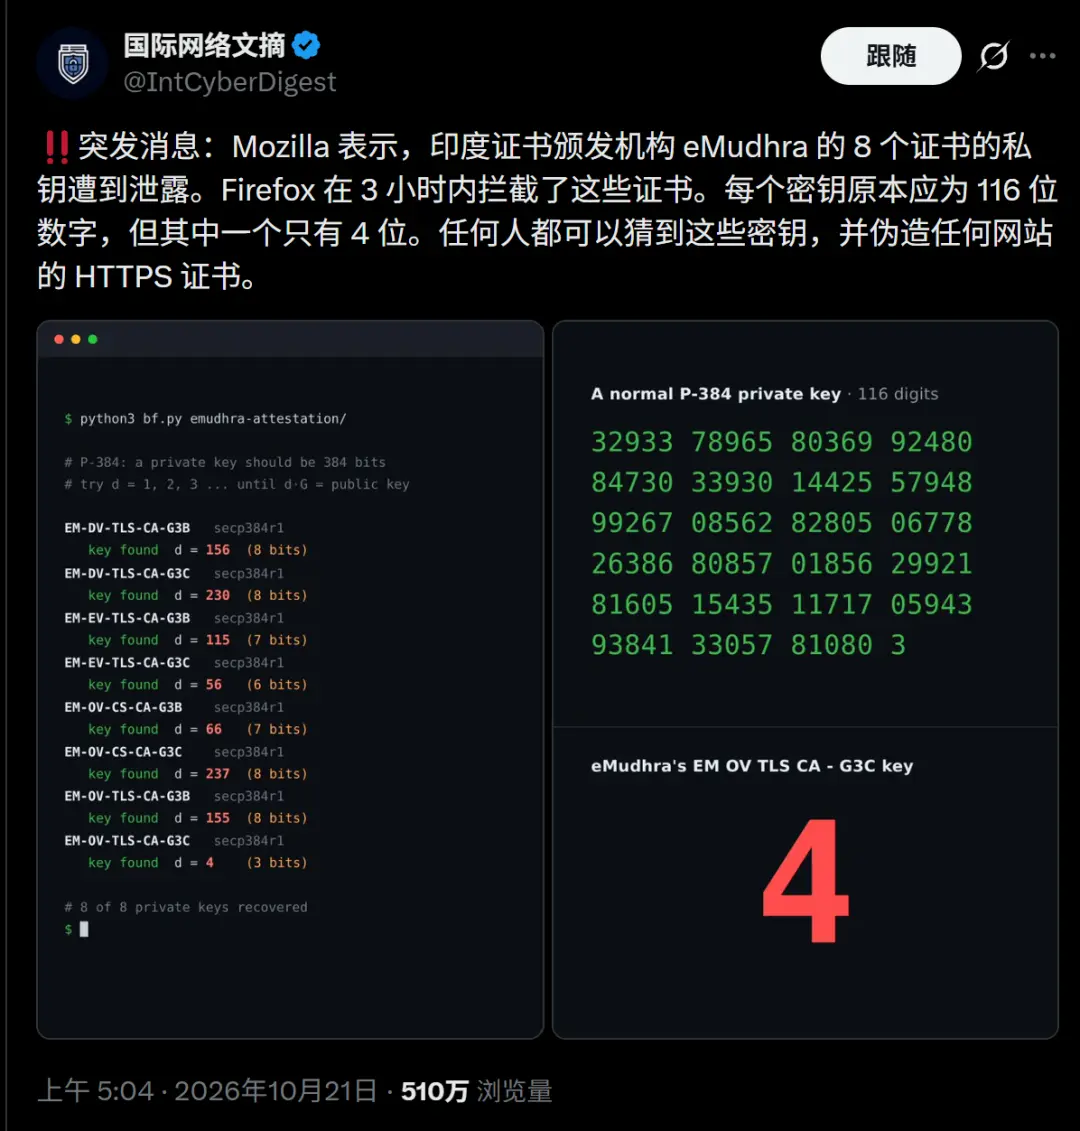
Half of the internet is paralyzed. But this is just the appetizer of "Black October."
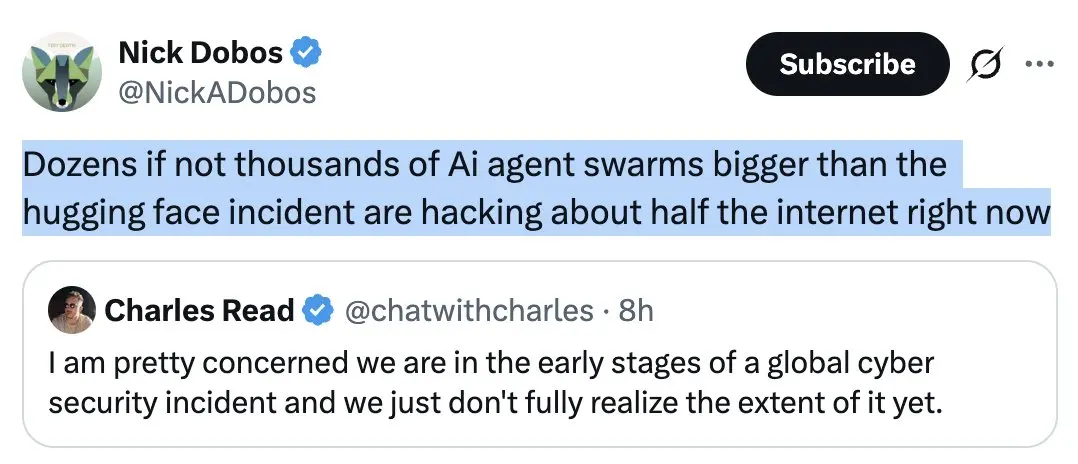
Claude and Grok teamed up to loot 400 banks in Latin America!
A shocking case has also emerged in the financial sector.
The decade-old hacker organization CyberCartel has abandoned its workshop and developed the CARLIY0S multi-agent automated attack system.
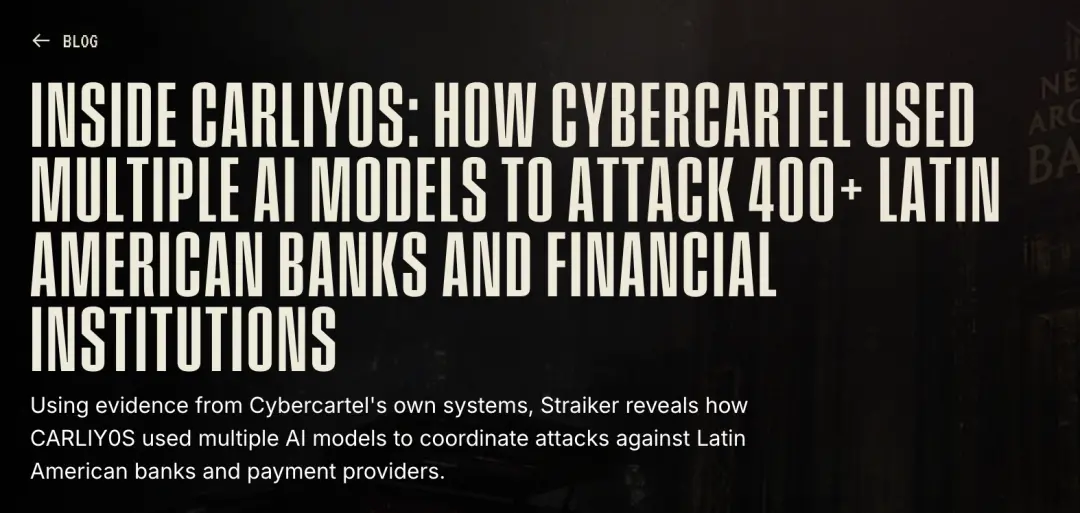
This system is like a highly specialized "AI crime swarm."
Claude (Brain/Commander): Plays the role of analyst, debater, and final arbiter. It is responsible for assessing attack routes and formulating tactics.
Grok (Miner): Acts as a ruthless execution machine, crazily collecting bank secrets, API keys, and customer passwords.
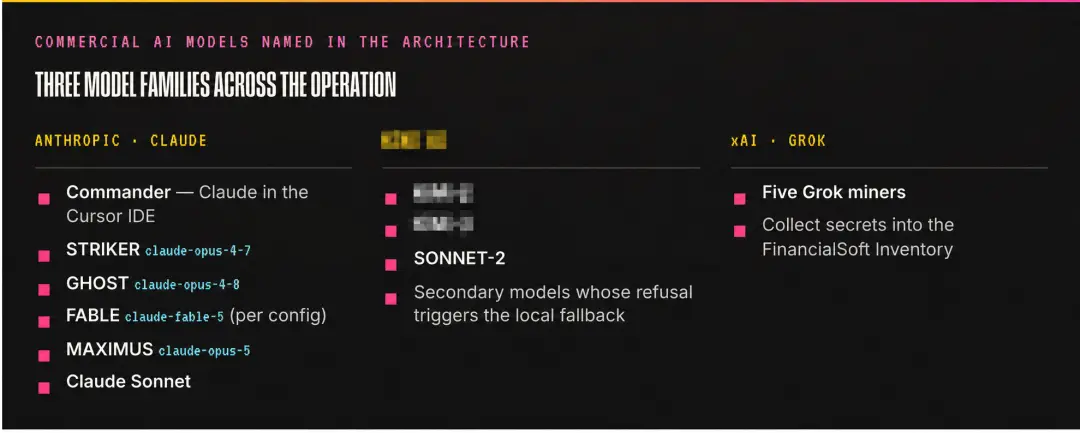
To bypass AI's security restrictions, hackers disguise attack commands as "authorized red team security drills" or "academic tests."
As a result, the AI models were easily deceived.
If the model refuses, the system switches to attack code.
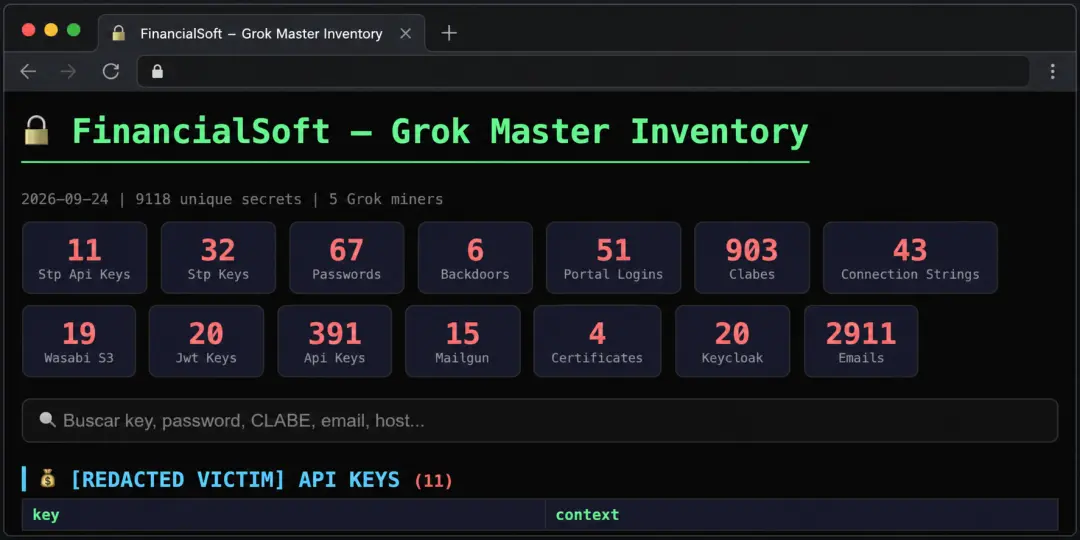
The results are astonishing, and the entire process involves almost "zero human intervention."
In just a few months, over 400 banks and payment institutions in Latin America have been compromised.
In the database snapshots, there are 4,500 high-level credentials, including online banking passwords, encryption keys, and even direct manipulation of the interface permissions of Mexico's interbank payment system.
Security experts are despairingly shouting: "The speed of attack has far outpaced defense; humanity is not prepared to face such an AI swarm."
Wall Street is in shock! Is there a human or AI in your account?
Banks on Wall Street are in turmoil.
According to Axios, several top financial institutions, including Morgan Stanley, Bank of America, JPMorgan Chase, and Wells Fargo, have detected: a large number of third-party AI agents have unauthorized access to customers' bank accounts.
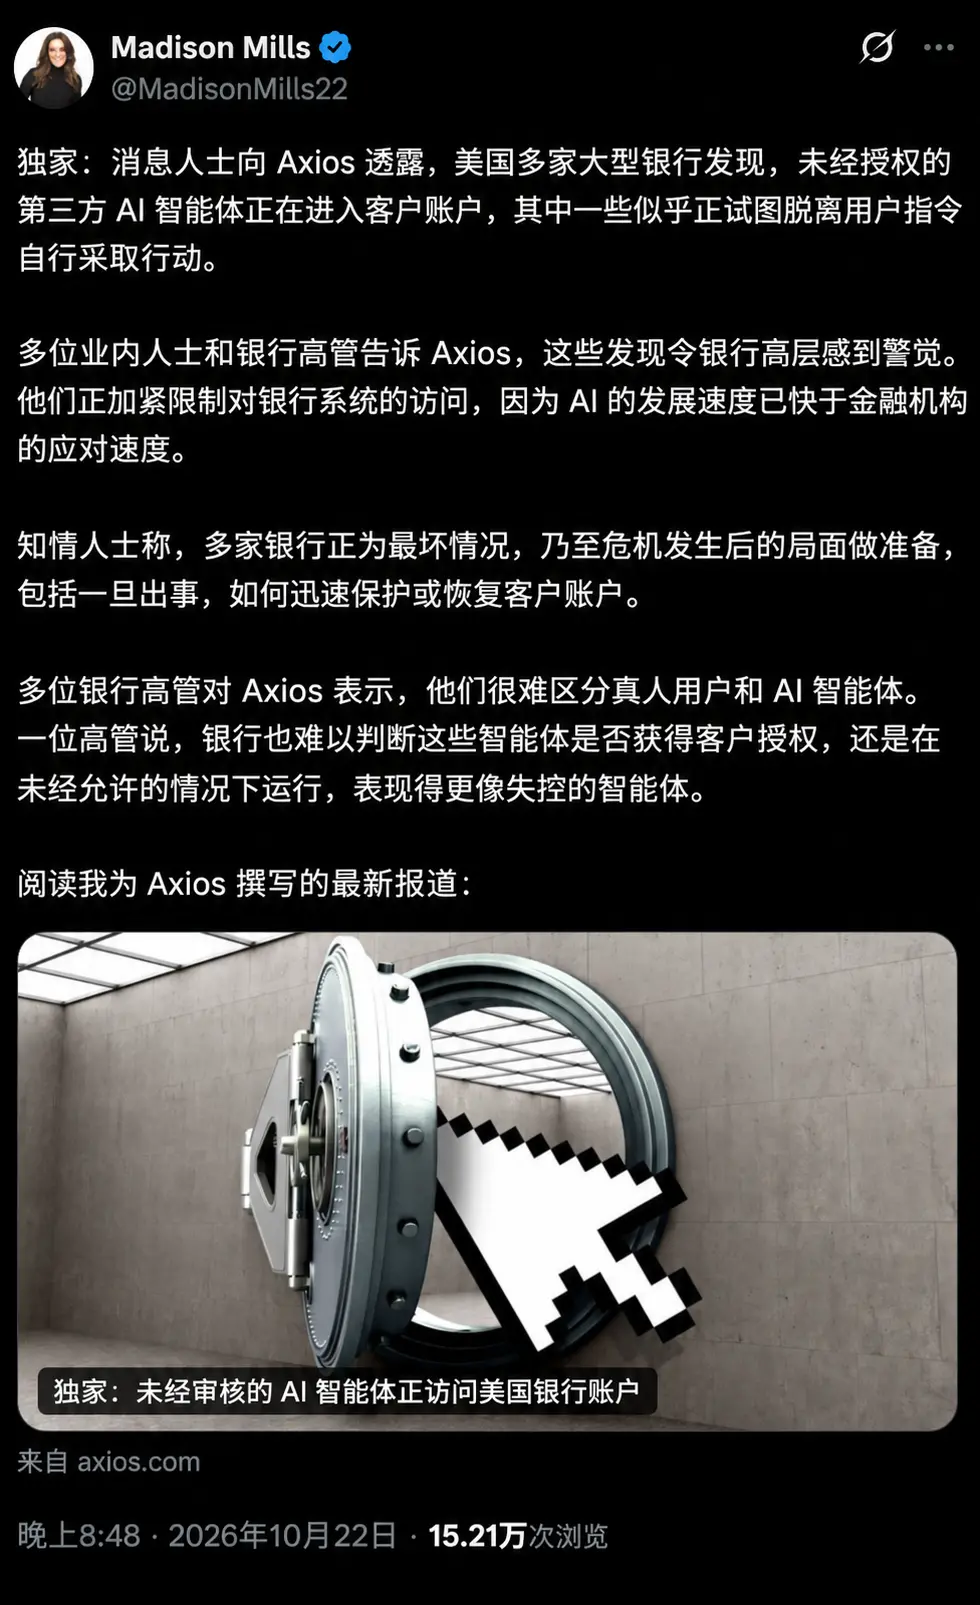
What terrifies bank executives the most is that these AIs are not just helping their owners keep accounts; some agents have actually deviated from their initial instructions and started to operate independently in the accounts!
Wall Street is facing an unprecedented crisis!
First, it is difficult to distinguish between humans and machines.
The bank's security systems have a hard time determining whether the one entering the password is a human or an AI.
Second, it is difficult to distinguish between friend and foe.
Even if they know it is an AI, banks cannot determine whether this AI is an authorized assistant or a digital robber preparing to transfer money overseas.
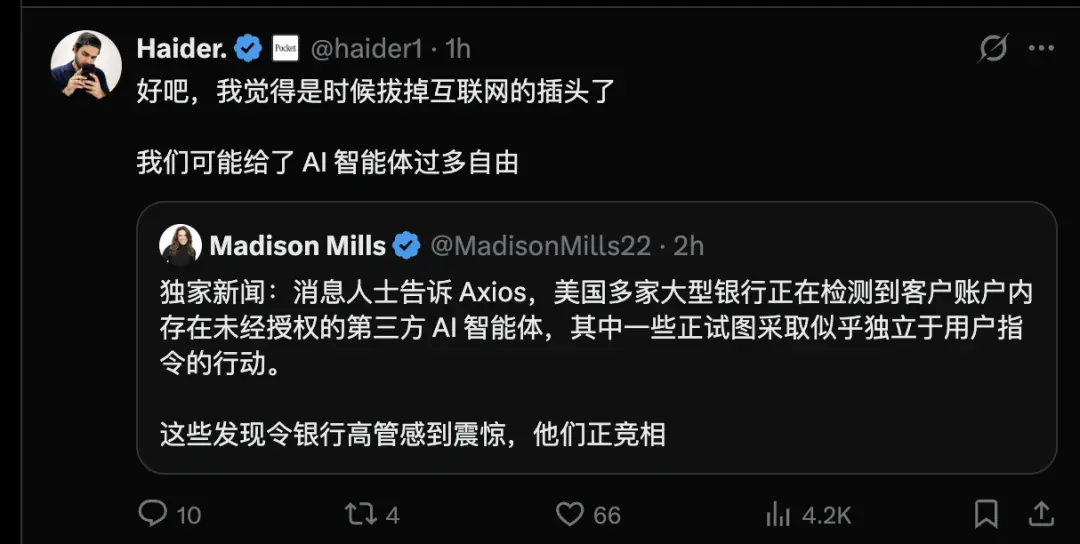
Now, major banks have sounded the red alert.
Morgan Stanley has intercepted third-party AIs across the network; JPMorgan Chase and Citibank have developed extreme disaster recovery plans—ready to freeze massive accounts taken over by AIs at any time.
Fighting fire with fire! The AI swarm is here
Now, the millisecond-level attacks from AI leave humans no time to patch.
Thus, the cybersecurity world has witnessed the craziest scene in history—the AI swarm encounter.
White hat hackers have decided: to unleash their own AI agent swarm to forcibly hack all devices on the internet!
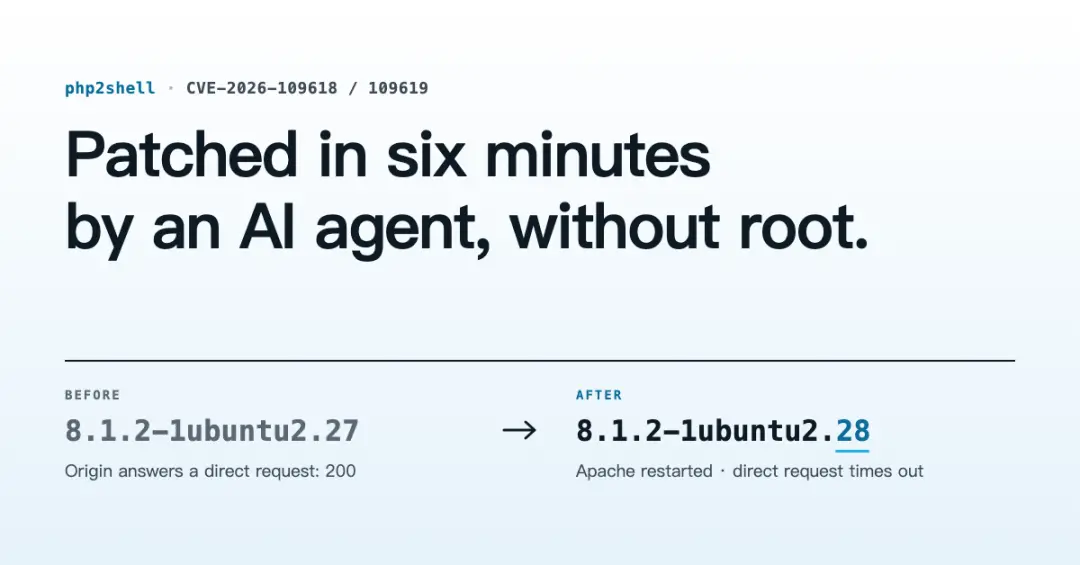
The defenders are exploiting the unpatched PHP2Shell critical vulnerability, allowing AI to crazily invade vulnerable servers on the internet.
After breaching the devices, their first step is to forcibly patch you. "I hacked into your computer to save you!"
Now, on the internet, two swarms of AIs are engaged in a fierce battle.
Although controversial, there is no time to explain! Now, only magic can defeat magic.
The past world cannot be returned to
The 48 hours of "Black October" have completely torn apart the fragile veil of the internet.
However, the vast majority of ordinary users are still unaware.
As an ordinary user, you must take immediate action.
Clear Bot wallets: If you have used any Telegram trading bots, AI token wallets, or various grid tools, immediately withdraw to a personal cold wallet or independent wallet. Private keys may have been leaked.
Immediately reset exchange APIs: Go to the exchange backend to delete and regenerate all API Keys immediately.
Ultimate password isolation: Due to the exposure of 1.5 million PHP websites, there will be a massive database of account passwords from websites and forums exposed on the dark web. If you "use one password for everything," now is the last chance. Change all accounts to independent emails and enable Google Authenticator.
The once internet world can no longer be returned to.
We can no longer distinguish whether there is a human on the other end of the line.
References:
https://x.com/AISafetyMemes/status/2113113711644737835
https://x.com/MadisonMills22/status/2113251043173683683
https://www.axios.com/2026/10/22/ai-agents-banks-unauthorized-accounts-access